NIST Cybersecurity Framework 2.0
A free framework, voluntary for most organisations, for governing, identifying and reducing cyber risk. Version 2.0 (February 2024) added a sixth function, Govern.
A community for restaurant groups, franchisees, ordering and payment providers and cyber leaders protecting multi-site food service.
Restaurant chains run many kitchens on shared point-of-sale, ordering, loyalty and supplier systems, often through franchisees and managed service providers. The hub focuses on keeping every location trading and every customer’s data safe.
Timely, food-sector context on emerging threats and defensive priorities.
Small, trusted conversations between operators, practitioners and partners.
Scenario-led sessions for testing decisions before a real incident.
Focused collaboration on common controls, dependencies and good practice.
Peer discussions designed for boards and operational leadership.
Useful outputs shaped by the people responsible for food operations.
Digital systems now sit inside the processes that keep products safe, production moving and customers supplied.
Card-skimming malware and stolen credentials can put payment data at risk in every location at once.
Disruption to apps, kiosks or delivery integrations can stop sales across the whole chain.
Shared IT, managed service providers and remote access give attackers a path between sites.
The frameworks organisations build on, and the rules worth knowing where they operate.
A free framework, voluntary for most organisations, for governing, identifying and reducing cyber risk. Version 2.0 (February 2024) added a sixth function, Govern.
The international standard for an information security management system. Organisations can be certified against it by an accredited certification body.
A series of standards for securing industrial automation and control systems — the operational technology that runs plants, farms and warehouses.
Why it matters
Helps secure connected production equipment without compromising availability.
Read moreThe card industry's security standard for any business that stores, processes or transmits payment card data. All of version 4's requirements have applied since 31 March 2025.
Why it matters
Every till, kiosk, ordering app and online checkout that takes cards sits inside its scope, at company-owned and franchised sites alike.
Read moreA personal data breach must be reported to the data protection authority within 72 hours of discovery where feasible, unless it is unlikely to put people at risk. The UK GDPR sets the same deadline.
Why it matters
Loyalty apps, online orders and reservations hold customer data, so a breach can start a 72-hour reporting clock.
Read moreRequires firms handling foods on FDA's Food Traceability List to record key data elements at critical tracking events such as shipping and receiving.
Why it matters
Restaurants receiving foods on FDA's list — leafy greens, fresh-cut produce, soft cheeses, shell eggs, many fish — must keep receiving records, and FDA can ask for them within 24 hours in an outbreak.
Read moreA starting point, not legal advice — which rules apply depends on where and how your organisation operates.
Bringing the right disciplines to the same table — from operators and producers to security practitioners and technology partners.
Be one of the first members of this hub — applications are open.
Member companies CSAFI adds to this hub will appear here.
Legislative coverage of the U.S. Farm and Food Cybersecurity Act, explaining proposed requirements for biennial cybersecurity assessments of the agriculture and food sector.
The foundational framework for managing cybersecurity risk — Govern, Identify, Protect, Detect, Respond, Recover. The common language most food-industry security programmes build on.
HTML version of the comprehensive open-access survey documenting 30 cybersecurity incidents (2011–2023) across the food and agriculture sector and introducing the Farmer-Centered AI (FCAI).
Comprehensive open-access review of 30 documented cybersecurity incidents across the food and agriculture sector (2011–2023), including ransomware, data breaches, and supply chain attacks, with analys
Microsoft guidance mapping Microsoft 365 and Azure security controls to the NIST Cybersecurity Framework to support compliance and risk management.
ASD's official cybersecurity portal providing the Information Security Manual (ISM), Essential Eight, Critical Infrastructure Uplift Program, threat intelligence, incident response, and cyber resilien
Australian Signals Directorate program enabling collaboration, cyber threat intelligence sharing, training, and resilience building between government, industry, academia, and critical infrastructure
Australia's central cybersecurity portal providing guidance, the Information Security Manual (ISM), Essential Eight, advisories, and cyber resilience resources for organizations.
ENISA's official portal providing cyber threat intelligence, sector threat landscapes, ransomware analysis, threat taxonomy, and emerging cyber threat information.
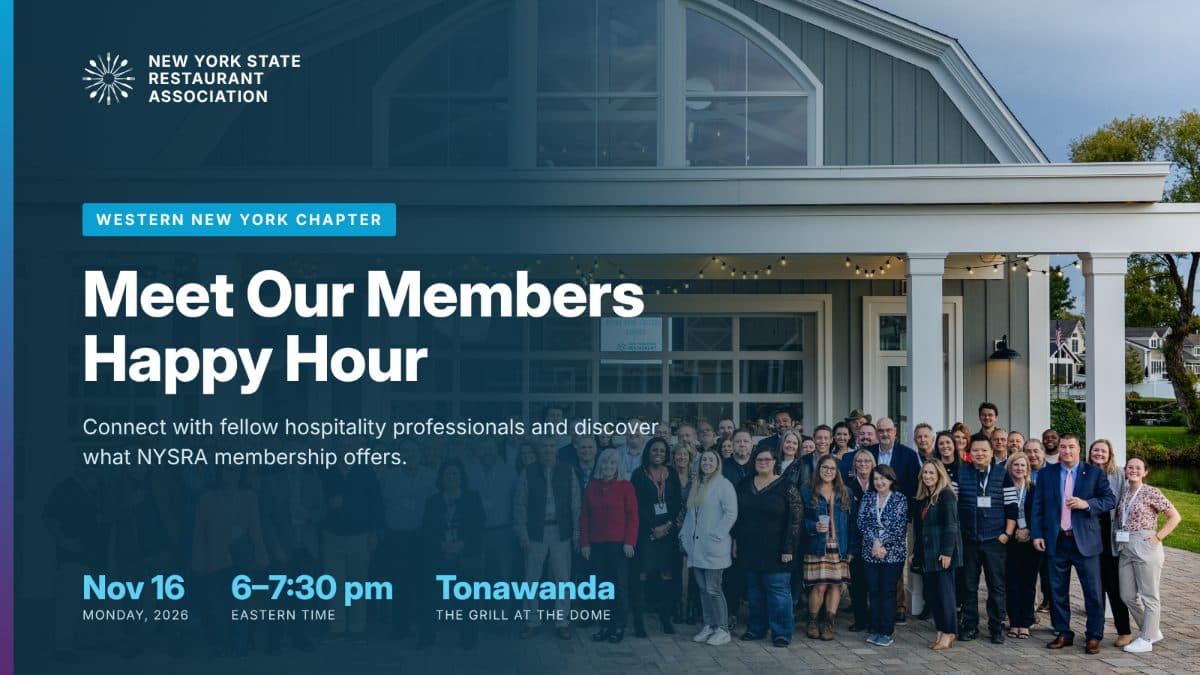
Price: Free
 New York State Restaurant Association (NYSRA)
Price: Free
New York State Restaurant Association (NYSRA)
Price: Free
 CSAFI
Price: Free
CSAFIJoin the people strengthening cybersecurity across the food ecosystem — before the next disruption tests us.